Alessia Gilardi
Regional Product Compliance Consultant
Alessia Gilardi is a GRC manager with extensive international experience in compliance, data protection, audit, and risk management. She specializes in turning complex legal requirements into practical solutions that support the business. She is certified by the International Compliance Association (ICA).
Key takeaways:
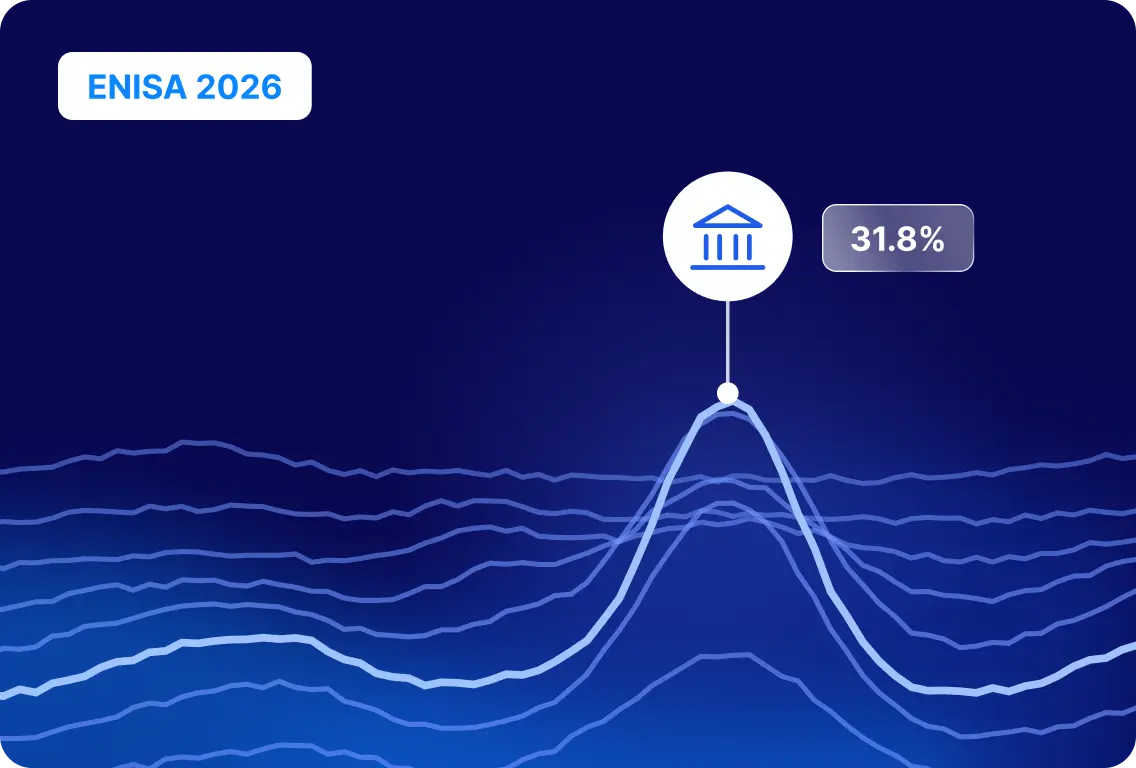
Public administration was the most targeted sector in the EU in 2025, with 31.8% of the 8,257 incidents ENISA recorded, almost four times the next sector, business services (8.5%).
Most of those incidents were hacktivist DDoS attacks, but ransomware hit municipalities in particular, and state-linked groups kept up espionage against government bodies.
ENISA counts public administration among the sectors in its "risk zone", where cybersecurity maturity falls short of how critical the sector is.
On 11 November 2026, about 6,300 of Italy's 7,476 state schools received the same hoax bomb threat by email, and schools in Scotland, Northern Ireland and Ireland got similar messages. No breach of school systems has been reported.
ENISA's findings become day-to-day practice when every risk and control has a named owner, incident procedures are rehearsed and evidence is kept current.
On the morning of 11 November 2026, school principals across Italy opened the same email: a bomb threat, sent to about 6,300 of the country's 7,476 state schools, according to Education Minister Giuseppe Valditara. Around 300 schools were evacuated. Prime Minister Giorgia Meloni said there was no sign of concrete danger, and Police Scotland treated similar messages to Scottish schools as hoaxes. No school systems appear to have been breached, but lessons were interrupted, and school leaders had to decide within minutes whether a threat was real.
The emails arrived just after ENISA, the EU Agency for Cybersecurity, published its latest assessment of cybersecurity in the Union. It confirms a pattern the agency has described for some time: public administration, which in Italy includes state schools, is the sector attackers target most in the EU, and its cybersecurity maturity hasn't kept pace.
What ENISA's 2026 reports say about public administration
Two ENISA reports from 2026 matter here. The ENISA Threat Landscape 2026, released in September, analyzes 8,257 incidents recorded in 2025. The 2026 Report on the State of Cybersecurity in the Union, released in November and prepared under Article 18 of the NIS2 Directive, assesses the period from July 2024 to July 2026.
Together, they show four things about public administration:
It is the most targeted sector. Public administration accounted for 31.8% of recorded incidents in 2025, ahead of business services (8.5%), transport (8%) and manufacturing (6.9%).
Volume isn't the same as impact. 81.8% of the incidents against the sector were ideology-driven DDoS attacks, which mostly make websites temporarily unavailable. The more serious threats are smaller in number: ransomware, which ENISA says primarily affected municipalities, and state-linked groups with a sustained focus on cyberespionage against government bodies.
Maturity lags behind exposure. The State of the Union report places public administration in its "risk zone": sectors that are more critical to society and the economy than their preparedness would suggest. ENISA describes the sector as newly regulated and at an early stage, with "reactive and uneven risk management and limited collaboration across the sector's entities".
Bodies start from different places. Central, regional and local administrations and municipalities of all sizes face their own constraints on resources and expertise, which ENISA says leads to varying maturity levels. It also lists public administration among the sectors where legacy systems are common and often difficult or very expensive to patch or replace.
Education doesn't appear as a sector of its own in the threat landscape, although one of its incident examples is an INC ransomware attack that disrupted digital services at Roma Tre University in Rome. ENISA's public administration threat landscape also lists educational systems among the targets of data-related attacks.
What the school email threats show
The 11 November emails were hoaxes. Valditara spoke of a strategy, Meloni said the threats aimed to generate alarm, and the Italian intelligence services and judiciary are investigating. Schools in Scotland and Northern Ireland had already received a similar wave in October.
The disruption still points to three weaknesses that go beyond schools:
Size doesn't limit exposure. The same email reached more than eight in ten Italian state schools in a single morning, the smallest as well as the largest.
Decisions under time pressure. Each school had to judge the threat, decide whether to evacuate and inform families within minutes.
Information has to travel fast. Schools in several countries received similar messages on the same day. How quickly that becomes shared knowledge decides how fast others can react, and ENISA finds collaboration between the sector's entities still limited.
A school can't stop a hoax email from arriving. How quickly it can verify a threat, who decides, and how parents hear about it all depend on preparation done beforehand.
What the rules expect from public bodies
How much of this is a legal requirement depends on the body and the country:
NIS2 in Italy: the Italian NIS2 law, D.Lgs. 138/2024, applies to the public administrations listed in its Annex III regardless of size, and classes central public administrations as essential entities. The ACN, Italy's national cybersecurity agency, notifies the organizations it considers in scope. Our article NIS2 Italy Deadline: Why Excel Is No Longer Enough covers the deadlines.
Incident reporting in Italy: Law 90/2024 requires central administrations, regions, metropolitan cities, municipalities with more than 100,000 inhabitants, local health authorities and other listed bodies to report incidents to the ACN within 24 hours, with a full notification within 72 hours.
Scotland: the Scottish public sector cyber resilience framework (version 2.0, December 2024) is issued to all public sector organizations by Scottish ministers and serves as guidance for audit and assurance.
Whether or not a school is directly in scope, the body that runs it often is: a ministry, a region or a municipality. The risks and controls have to be managed where the responsibility sits.
What a structured control system looks like
ENISA's public administration threat landscape recommends practical measures: multi-factor authentication, backups with offline copies and regular restore tests, prompt patching, DDoS protection for public portals, exercises, and more information sharing. Turning that list into practice takes a system that answers five questions at any time:
What are we responsible for? The frameworks and laws that apply, from NIS2 to national rules and internal standards, with their requirements in one place.
What could go wrong, and how badly? A risk register that includes mass-disruption scenarios such as DDoS, ransomware and hoax threats, with inherent and residual scores and a named owner for each risk.
What have we put in place? Controls with owners and a status, linked to the risks they reduce and the requirements they meet.
Can we prove it? Evidence for each control, such as policies, restore test results and training records, with a date that shows when it needs renewing.
What happens when something goes wrong? Incident procedures with clear roles, reporting deadlines and lessons learned, checked through internal audits.
For a ministry responsible for thousands of schools or a region with dozens of agencies, this structure has to work across many bodies at once. A shared model helps: one framework with its controls, policies and risks, which each body adapts instead of starting from scratch.
How Formalize helps public bodies
Formalize brings compliance, risk and internal audit together in one platform, so a public body can show what it has done and who is responsible:
Compliance Blueprints: start from the NIS2 Compliance Blueprint in the Formalize Marketplace, with its controls, policy templates, risk examples and recurring tasks, or from ISO 27001 with a Statement of Applicability, then adapt the setup to your organization.
Risk register: inherent and residual scoring, with risks linked to the assets, processes, systems and suppliers they affect.
Owners and tasks: controls and recurring tasks with responsible people and deadline notifications.
Incidents: an incident register, with notification deadlines set up in workflows and shown as met or missed.
Policies and evidence: policies with approval flows and staff acceptance tracking, and evidence with validity periods and version history.
Internal audits: the Audit module, with findings tracked to an owner, a target date and independent sign-off.
Several bodies, one account: entities such as schools or agencies in one account, with permissions that can be limited to a user's own entities, and an interface available in Italian and 13 other languages.
Formalize helps public bodies organize and document the work. It doesn't replace the technical measures themselves or the judgment of the people responsible.
See how a public body runs NIS2 in Formalize
We'll show you how the NIS2 Compliance Blueprint connects requirements, risks, controls, owners and evidence across several entities.
Frequently asked questions
This article reflects information available on 11 November 2026. It is general information, not legal advice.