Our blog

Resources and Insights

What changed in European compliance, what it requires, and what to do about it.

Frameworks

GDPR Compliance Means Being Able to Prove It

The principles, a 10-step checklist, and what changes in 2026 and 2027.

Maurice Müller

Maurice Müller

07.10.26

News & Analysis

When an AI Agent Causes a Data Breach

Why incident response and AI governance can no longer run separately.

Alessia Gilardi

Alessia Gilardi

29.09.26

Risk & Governance

Data Governance: Who Decides What Happens to Your Data

Frameworks, roles, and the steps to turn data rules into daily practice.

Maurice Müller

Maurice Müller

29.09.26

Frameworks

Cyber Resilience Act: The New 24-Hour Reporting Rule

Who it applies to, what it covers, and how it overlaps with NIS2 and GDPR.

Àngela Vercher

Àngela Vercher

28.09.26

Frameworks

DORA Regulation: What Still Needs Proving Now

The five pillars, the penalties, and what changed since the deadline.

Maurice Müller

Maurice Müller

24.09.26

News & Analysis

When Verification Fails: A GDPR Breach Case

The control that would have stopped it, and why most policies lack it.

Laura Santeusanio

Laura Santeusanio

23.09.26

Frameworks

What Is a DPIA? GDPR's Privacy Risk Assessment, Explained

Discover how to spot Article 35 triggers, the 7 steps, and what to include.

Maurice Müller

Maurice Müller

21.09.26

Frameworks

NIS2 in Italy: "Compliant on Paper" Won't Survive October

The 10 required measures, the fines, and how to close the gap in time.

Laura Santeusanio

Laura Santeusanio

18.09.26

Platform

Compliance Management Software: What to Look For

What the software does, the real benefits, and how to compare platforms.

Maurice Müller

Maurice Müller

16.09.26

Risk & Governance

What Is AI Risk Management?

Main risk types, the NIST framework, and a 6-step process to follow.

Maurice Müller

Maurice Müller

14.09.26

Risk & Governance

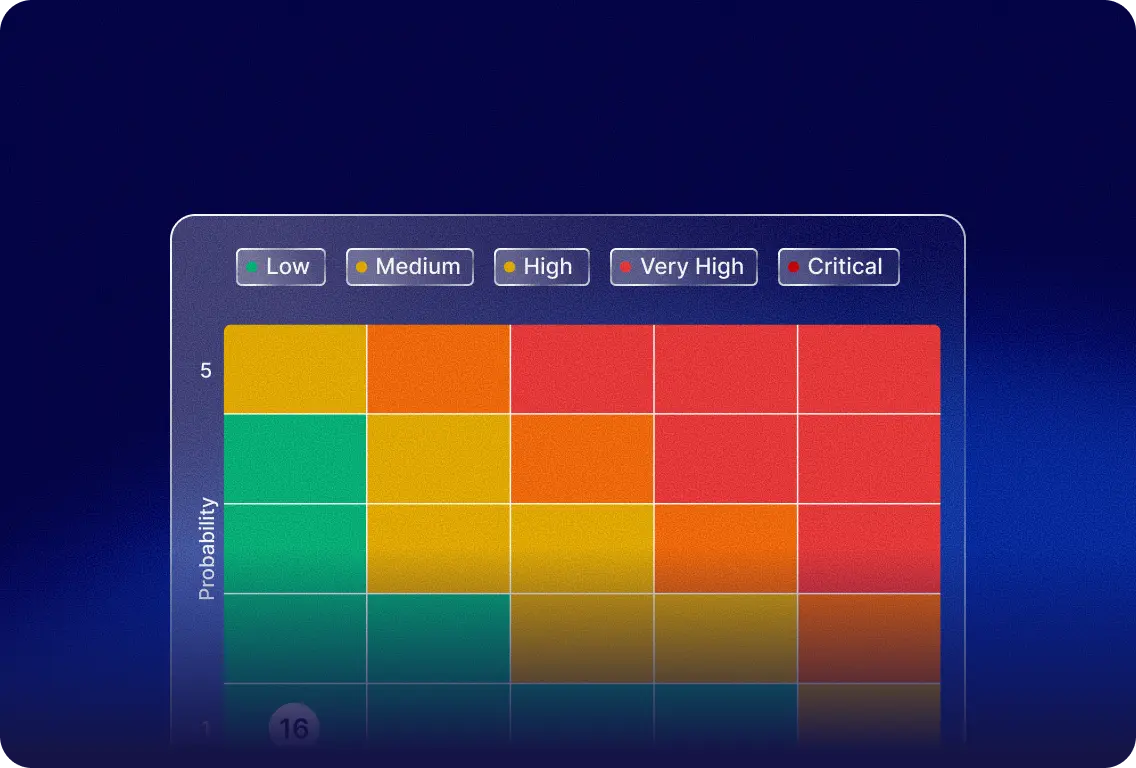
What Is a Risk Matrix? Scoring Explained

How likelihood and impact combine into a score, with a 5x5 example.

Maurice Müller

Maurice Müller

09.09.26

Risk & Governance

What Is Supplier Risk Management? A Practical Guide

How to assess, score, and monitor supplier risk, step by step.

Maurice Müller

Maurice Müller

04.09.26

Platform

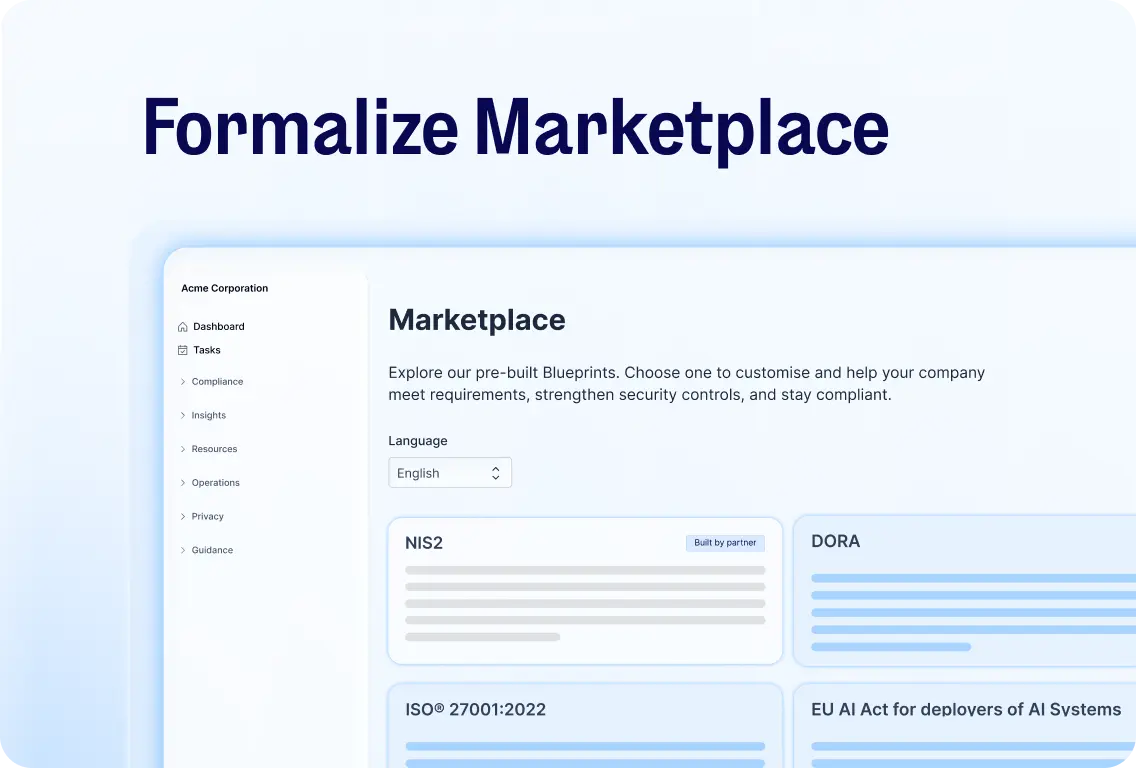
Formalize Marketplace: How Blueprints Work

Partners co-build ready-to-deploy blueprints, so you skip the blank page.

Maurice Müller

Maurice Müller

02.09.26

Risk & Governance

Risk Management Frameworks: Types, Steps & Examples

NIST, ISO 31000, or COSO: compare the frameworks and pick one that fits.

Maurice Müller

Maurice Müller

01.09.26

Frameworks

NIS2 Requirements: Key Pillars & Checklist

What NIS2 actually requires, and how to check where your organization stands.

Maurice Müller

Maurice Müller

25.08.26

Platform

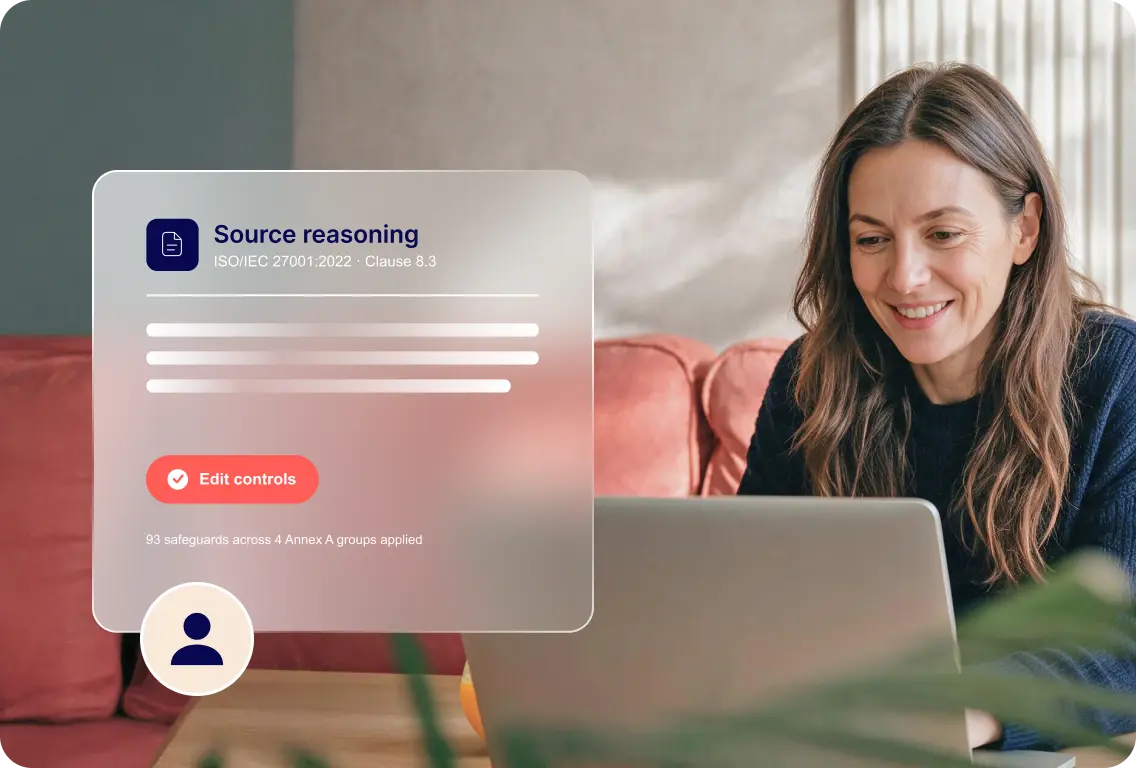
Your Controls Were Right. Are They Still?

AI that reads the actual ISO 27001 standard, not just summaries about it.

Maurice Müller

Maurice Müller

24.08.26

Platform

Stop Digging for Answers. Start Asking.

Your compliance records can finally answer questions, not just sit there.

Maurice Müller

Maurice Müller

24.08.26

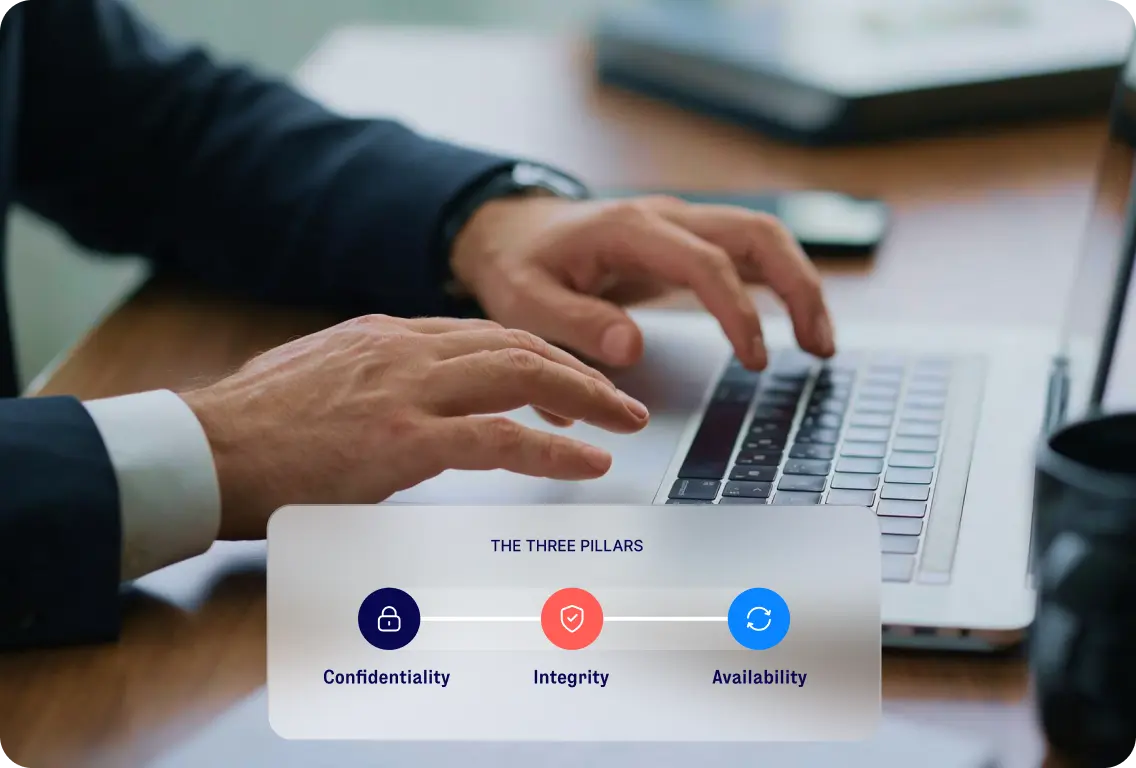
Person typing on a laptop, with an overlay showing the three pillars of information security: confidentiality, integrity, and availability.
Frameworks

What is ISO 27001? ISMS Standard & Compliance Explained

ISO 27001 is the international standard for managing information security risk.

Maurice Müller

Maurice Müller

20.08.26

Frameworks

EU AI Act: What the Digital Omnibus changed, and what it means for your organisation

The EU AI Act's Digital Omnibus has extended key compliance deadlines for high-risk AI systems. The headline is easy to misread: this is not a pause. The obligations remain. The timeline shifted.

Maurice Müller

Maurice Müller

18.08.2026

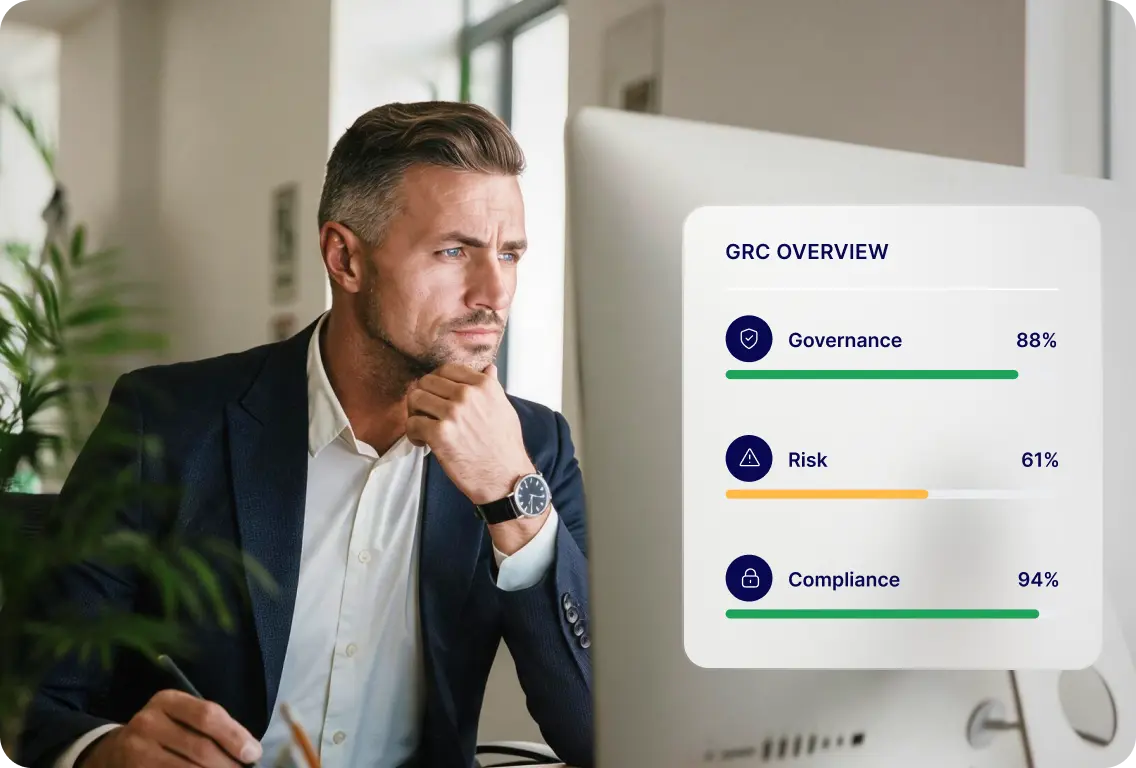
Professional reviewing a GRC dashboard showing governance, risk, and compliance metrics.
Risk & Governance

What is GRC? Governance, Risk, and Compliance Explained

GRC stands for Governance, Risk, and Compliance. The GRC meaning goes beyond the acronym: it describes how organisations structure their internal rules, manage uncertainty, and meet external regulatory requirements, not as three separate workstreams, but as one connected approach.

Maurice Müller

Maurice Müller

31.07.2026

Team working in a meeting room, with a colleague holding a laptop in the foreground.
Frameworks

What is NIS2? The EU cybersecurity directive, and what it means for your organization

NIS2 is the EU's updated directive on network and information security. It sets binding cybersecurity requirements for organizations across critical sectors in Europe, and since October 2024, it is in force.

Maurice Müller

Maurice Müller

31.07.26

Book a demo