The audit tool built on IIA standards
Run every audit on the controls, risks, and evidence you've already mapped. No spreadsheets, no re-collected evidence, no disconnected trackers.




Internal audit today
Three questions, and the answers we keep hearing
“How many tools does your audit touch?”
Excel for planning, email for questions, a shared drive for evidence. Months later, the trail behind a conclusion is hard to find.
“How do you prove a control works?”
Email threads, Drive folders, and a fresh spreadsheet export. The evidence already exists, but it gets collected again every time.
“How do you know a finding got fixed?”
Chasing owners and reporting status by hand. Nothing confirms the work is done, so items stay open or quietly get closed on trust.
A better answer to all three
Instead of spreadsheets, inboxes, and manual follow-up, the whole audit runs in one place. Here's what one of our partners noticed first.
"The Audit module makes it easy for us to trace the links between audit subjects, requirements, controls, and evidence, all the way to the final audit report.”
Erhard Christelbauer
Conseiller principal GRC , Bonafide
The manual way
-
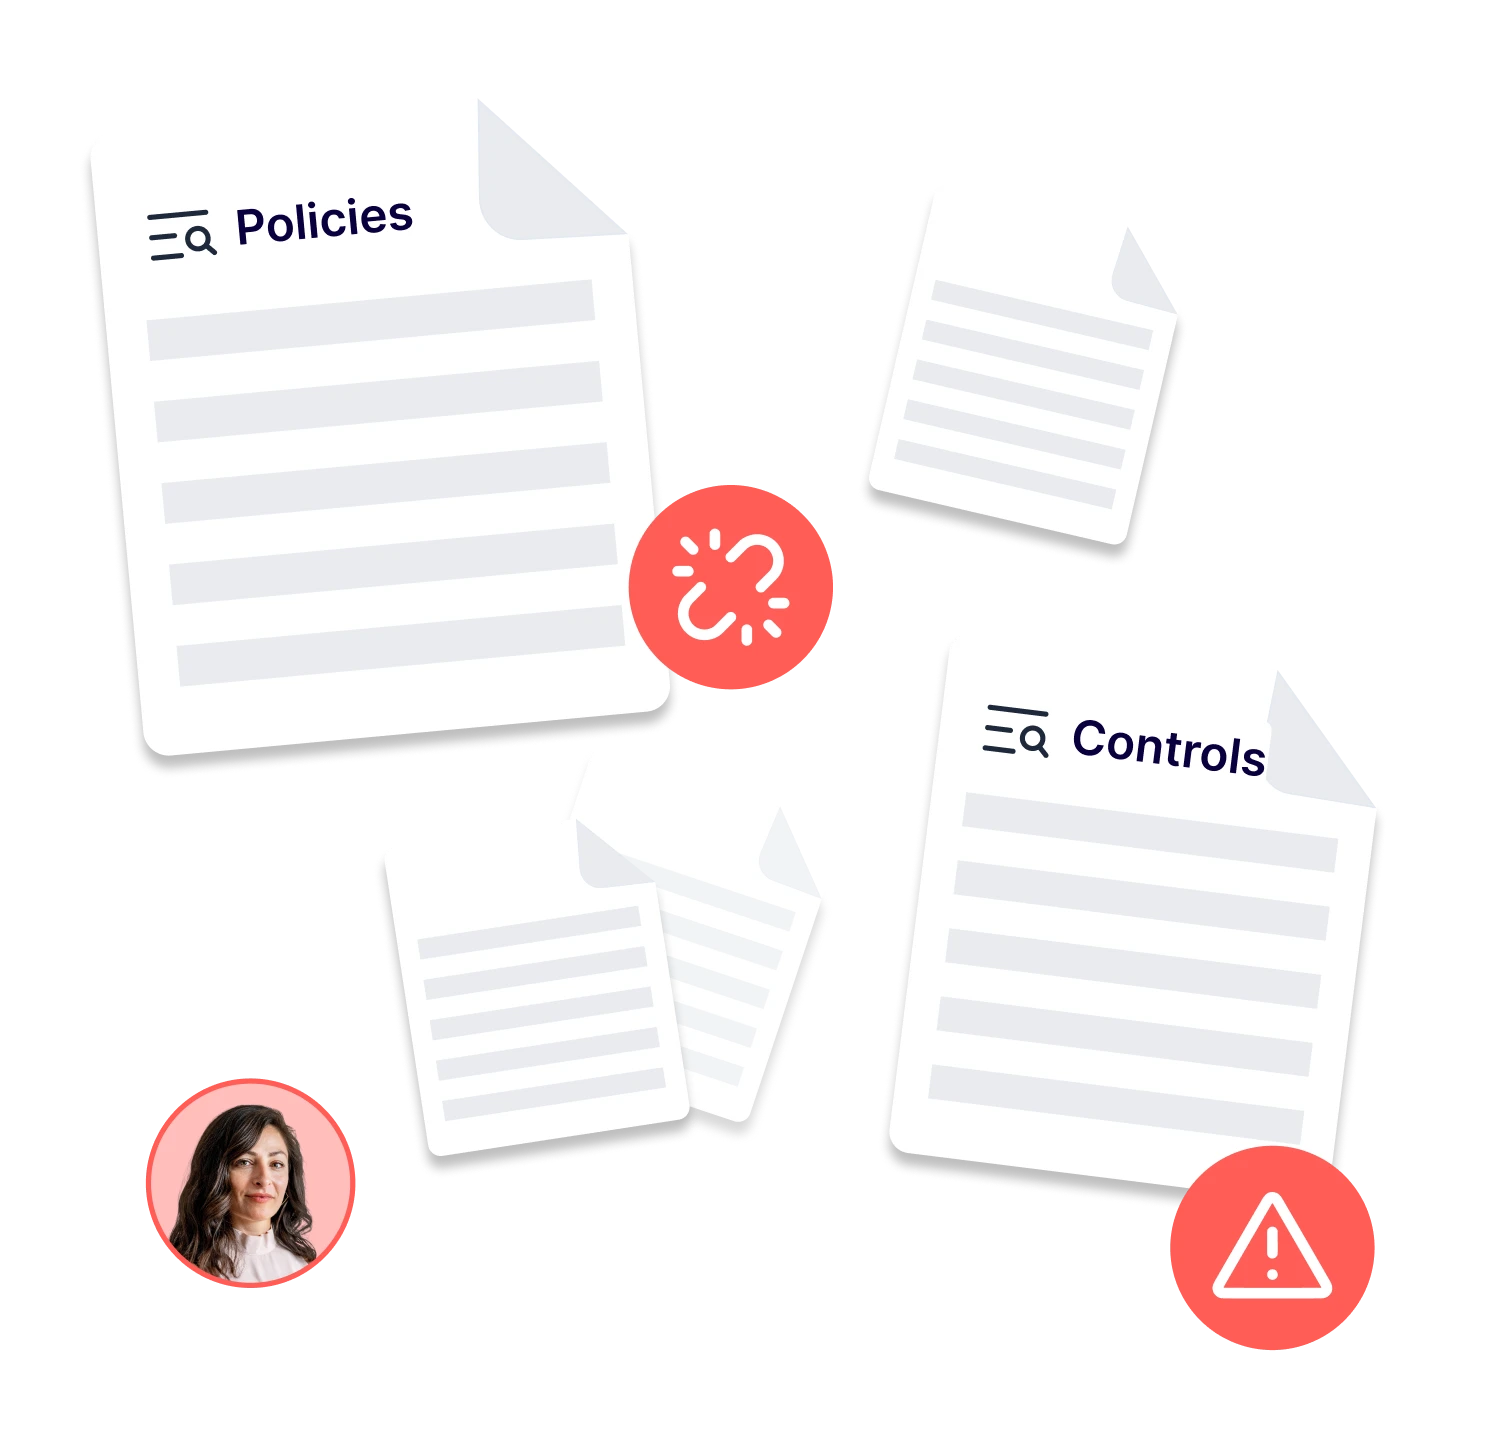
The scope sits in a long Excel list, the plan on a calendar or Kanban board. Nothing connects the two.
-
Evidence gets collected again for every audit, from inboxes, shared drives, and last year's exports.
-
Findings land on a tracker. Someone chases the owners, and anyone can mark a fix as done without a check.

The Formalize way
-
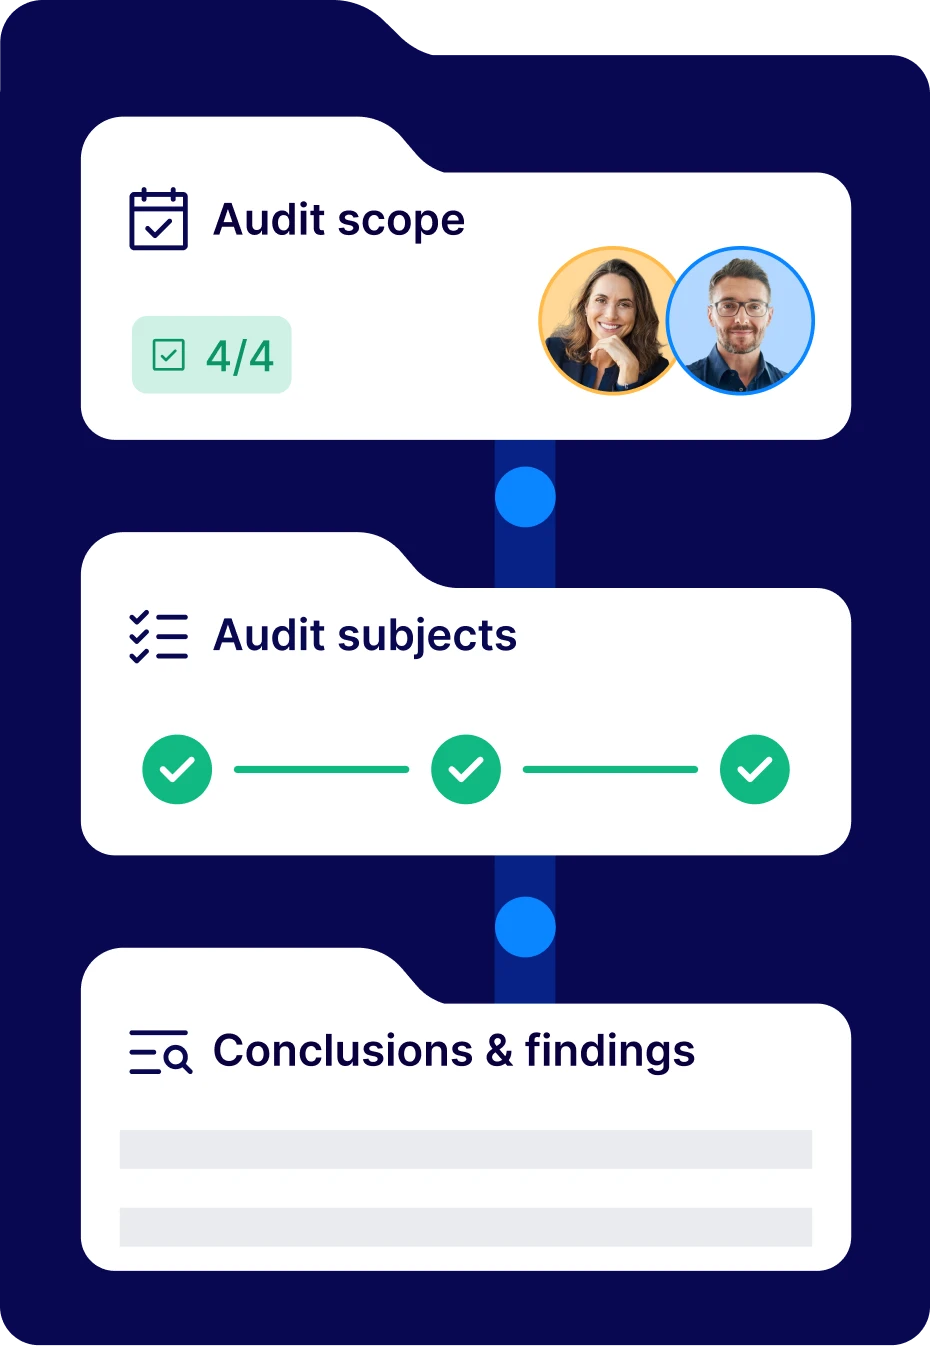
One lifecycle from scope to follow-up, structured to IIA Standards. Every step on the same audit trail.
-
Evidence links to controls, risks, suppliers, and almost any other record. Nothing gets collected twice.
-
Findings stay on the control, risk, or asset they affect, with an owner, a deadline, and independent sign-off.

Run the audit where your compliance work already lives
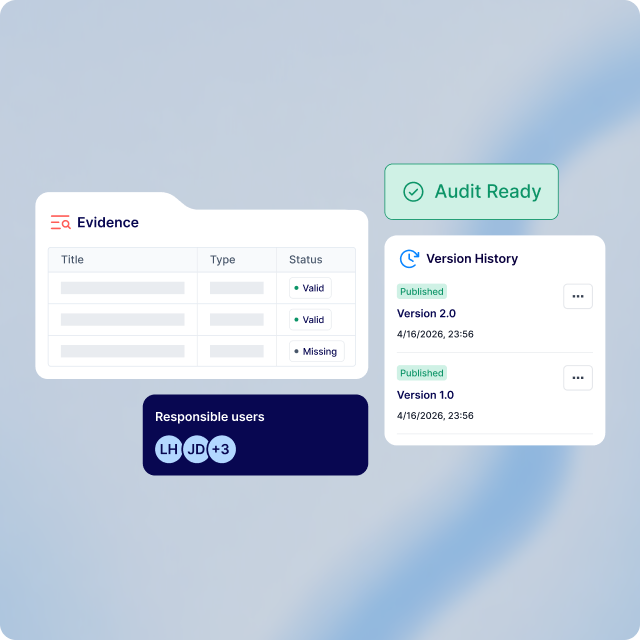
Audit lifecycle
A structure every auditor recognizes
Planning, scoping, fieldwork, conclusions, and follow-up run in one place, structured to the IIA Global Internal Audit Standards. When someone asks how you got there, the path is on record.
-
Clear roles: Audit Organizers plan, Lead Auditors own the process, and Field Auditors assess, each with their own access.
-
Your way of working: the audit moves through your team's usual steps, and follow-up can start while it's still running.
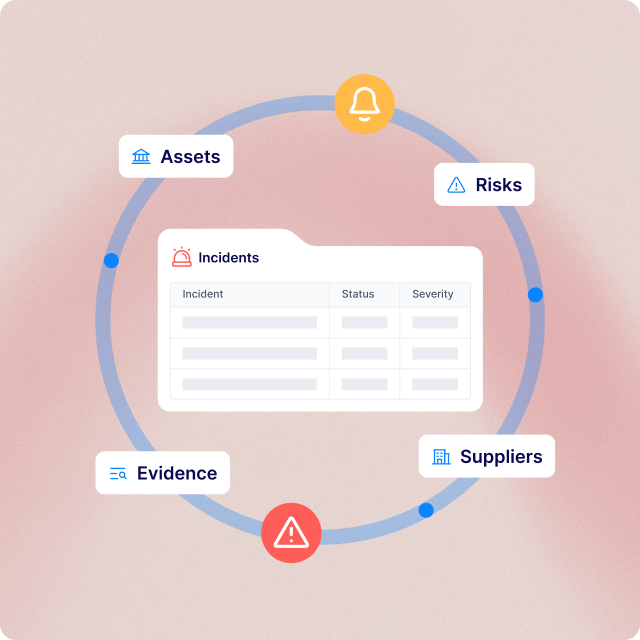
Connected data
Evidence that's there before anyone asks
Start an audit from a framework, a set of risks, or the assets and suppliers you manage, using live data instead of a copy. What you find flows back to the rest of your compliance work.
-
Straight from the source: each item links directly to the control, risk, or other record it supports, with no re-upload.
-
Flexible scope: combine different subjects in one audit, such as a department, a supplier, and the risks they carry.
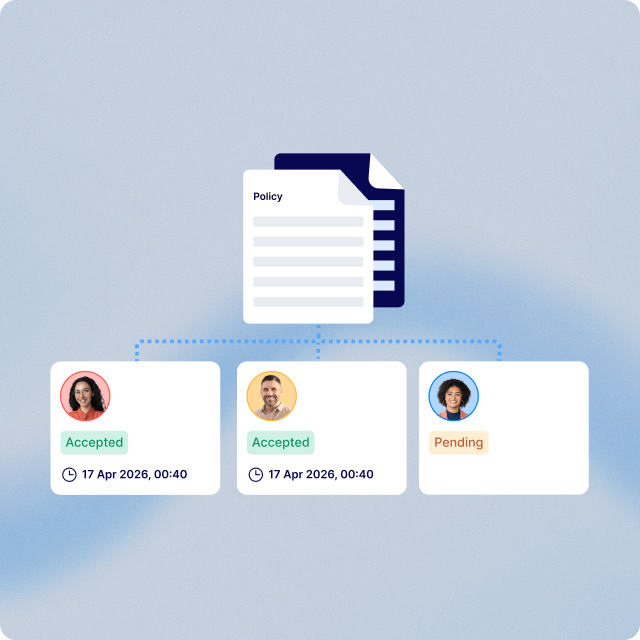
Remediation
Findings that get closed, not just logged
Each one is tied to the audit subject it affects and can turn into an action plan. Follow-up starts while the audit is still running and continues after it ends, so nothing gets lost.
-
Structured by default: every record captures the criterion, condition, root cause, and effect, as the IIA Standards describe.
-
Closed with a check: each fix gets an owner and a target date, and needs independent sign-off before it counts as resolved.
Built for a multi-framework reality
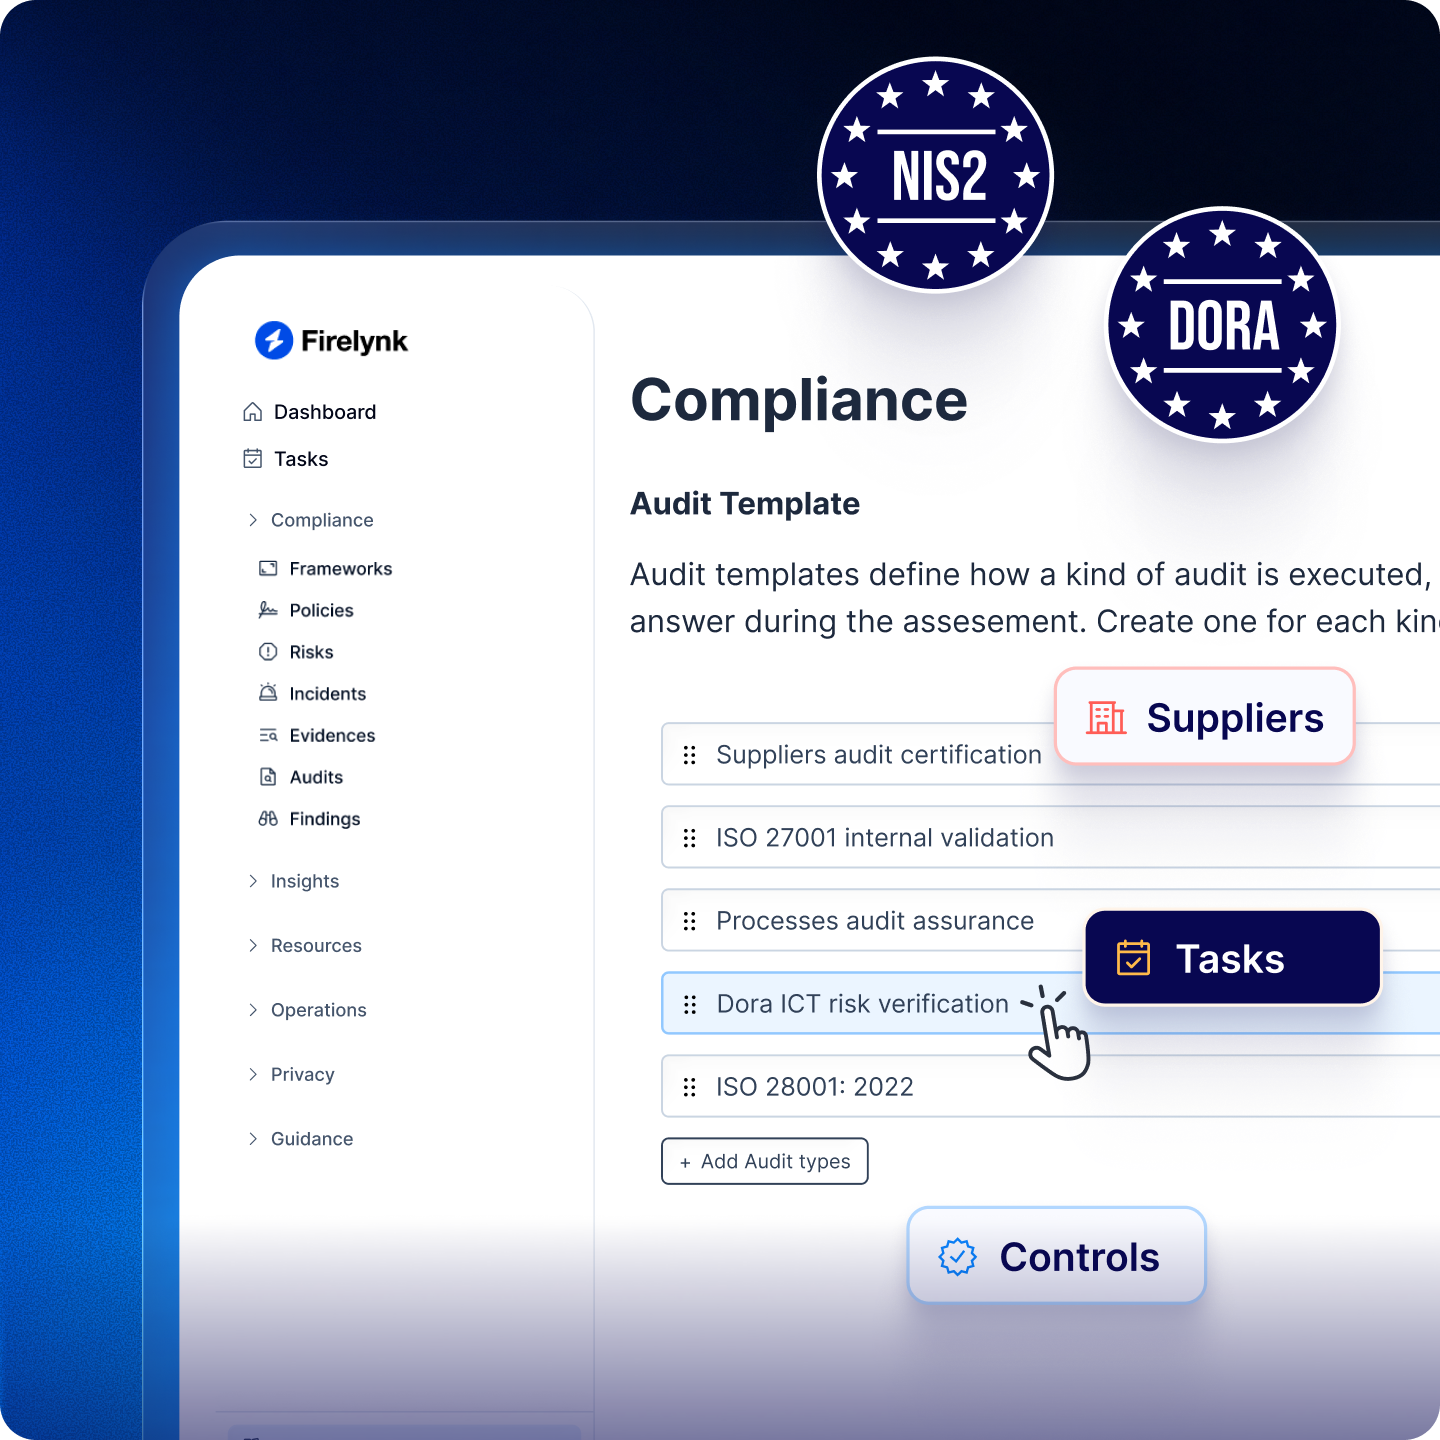
Regulations like GDPR, NIS2, and ISO 27001 don't exist in a vacuum. Formalize links your audit workflows directly to your broader compliance and security requirements, keeping your controls aligned across every framework from a single platform.
1 / 4
Your audit findings stay in the right hands
An audit gathers findings and evidence you don't want sitting in the wrong inbox. Formalize is certified to ISO 27001, the same standard many of our customers are audited against. All data is hosted in the EU, in Frankfurt and Dublin, and access is set by role, so each person sees only their part of the audit, from planning to fieldwork to sign-off.